8.8 million records leaked – why your Dutch small business must check data‑partner risk
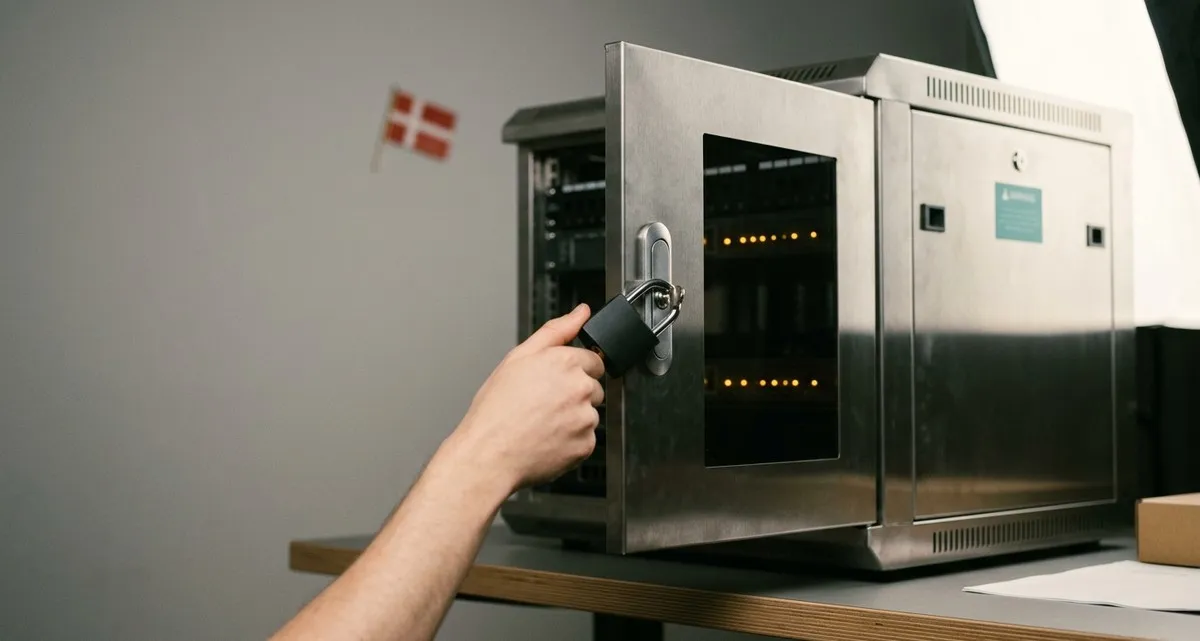
The leak that should worry every Dutch small business
When a private firm in Denmark abused its lawful access to the country’s Central Population Register (CPR), the personal data of 8.8 million people – more than Denmark’s entire population – was exposed. For a Dutch small‑business owner, the headline may feel distant, but the lesson is clear: a trusted third‑party data provider can become a single point of failure. If that partner is compromised, your customers’ details, your payroll information, or your sales records could be at risk too. The incident highlights data‑partner risk that any small business should assess.
What the Danish breach teaches about data‑partner risk
- Who was affected? An unnamed private company, authorised under Danish law to query the CPR, used its access to pull millions of records. The data included names, addresses, CPR numbers (the Danish equivalent of a social‑security number) and other identifiers.
- How was the breach discovered? The CPR administration noticed irregular activity on 2 October 2026 and, after a weekend of investigation, confirmed that the data had been exfiltrated.
- Why so many records? The CPR contains about 11 million entries, including people who have died or moved abroad. That explains why the leaked total exceeds the country’s current population of roughly 6 million.
- What is being done? The Danish authorities blocked the firm’s access, involved the Data Protection Agency and the police, and are debating whether to issue new CPR numbers for affected citizens.
The core problem wasn’t a technical flaw in the database; it was excessive, poorly‑controlled access granted to a third‑party vendor.
Why data‑partner risk matters to Dutch small businesses
Most Dutch small businesses rely on external services for tasks that involve personal data:
- a payroll provider that needs employee bank details,
- a CRM system that stores customer contact information,
- a marketing platform that processes email addresses for newsletters.
If any of those partners can pull more data than they truly need, a breach on their side instantly becomes your breach. The Danish incident shows how a “small” vendor, given broad rights, can inadvertently become a massive data‑leak conduit.
For a Dutch small business, the consequences are concrete:
- Regulatory fines – GDPR penalties can reach up to €20 million or 4 % of annual turnover.
- Loss of customer trust – a data breach often leads to churn and negative press.
- Operational disruption – you may need to reset passwords, re‑issue IDs, or even halt services while the breach is investigated.
In short, the security of your business is only as strong as the security of the partners you trust.
A three‑step checklist to protect yourself
1. Audit your data partners
- Create an inventory – List every external service that processes personal data, from cloud storage to invoicing tools.
- Verify legal basis – Ensure each partner has a clear, documented justification under GDPR for the data they handle.
- Review contracts – Look for clauses that require the partner to follow least‑privilege principles, to notify you of breaches, and to allow you to audit their controls.
2. Enforce least‑privilege access
- Limit data fields – Only give partners the exact fields they need. For example, a payroll service may need bank account numbers but not home addresses.
- Use role‑based permissions – Assign roles that restrict what each vendor can see or change.
- Regularly rotate credentials – Change passwords, API keys or certificates at least annually, or sooner after a staff change at the partner.
3. Implement continuous monitoring
- Set up alerts – Use tools that notify you when a partner accesses data outside normal business hours or exceeds typical query volumes.
- Log all data transfers – Keep a secure audit trail of who accessed what, when, and why.
- Conduct periodic tests – Run simulated breach scenarios (penetration testing) that include your third‑party connections.
By treating every vendor as a potential weak link and applying these steps, you dramatically reduce the chance that a breach elsewhere becomes yours.
FAQ
Q: How often should I audit my data‑partner risk?
A: Conduct a full audit at least once a year, and whenever you add, remove, or significantly change a service that handles personal data.
Q: What if a vendor won’t share data‑partner logs?
A: GDPR gives you the right to request evidence of how personal data is processed. If a vendor cannot provide satisfactory logs, consider switching to a provider that offers transparent monitoring.
Q: Can I manage data‑partner risk without IT expertise?
A: Yes. Start with a simple spreadsheet inventory, use built‑in permission controls in the SaaS tools you already use, and ask your IT service provider to help set up alerts and logging.
Keep your business safe with a managed risk assessment
Even with the best intentions, keeping track of every data‑partner can be overwhelming. At IT Move NL we specialise in Security & Protection for small businesses. Our managed data‑partner risk assessment includes:
- a full audit of all third‑party connections,
- implementation of least‑privilege controls tailored to your operations, and
- 24/7 monitoring with instant alerts if something looks out of the ordinary.
Don’t let a “small” vendor become the next headline. Contact us today for a complimentary risk review and make sure your data remains under your control.
Sources:
He/Him · AWS Certified Solutions Architect | Cloud Engineer @ Essent
Cloud Engineer at Essent B.V. with 10+ years of experience in the tech industry. AWS Certified, passionate about serverless architectures, Infrastructure as Code, and DevOps. Proficient in TypeScript, Python, and Terraform. Based in Amersfoort, Netherlands.
STAY IN THE LOOP
// Cloud, AI & DevOps insights — straight to your inbox.
No spam. Unsubscribe anytime.
// Related articles
Need help with your cloud infrastructure?
Our team of experts is ready to help you navigate the complexities of modern cloud architecture.
Get in Touch