Hackers arrested: what supply‑chain attacks mean for your business
Why the arrests matter: the rise of supply‑chain attacks
Australian authorities announced this week that two men suspected of belonging to the notorious TeamPCP hacking group have been arrested and charged with multiple offenses. Over the past nine months the group carried out a relentless supply‑chain campaign that infected more than 1,000 organisations worldwide, compromising everything from open‑source scanners to developer toolkits.
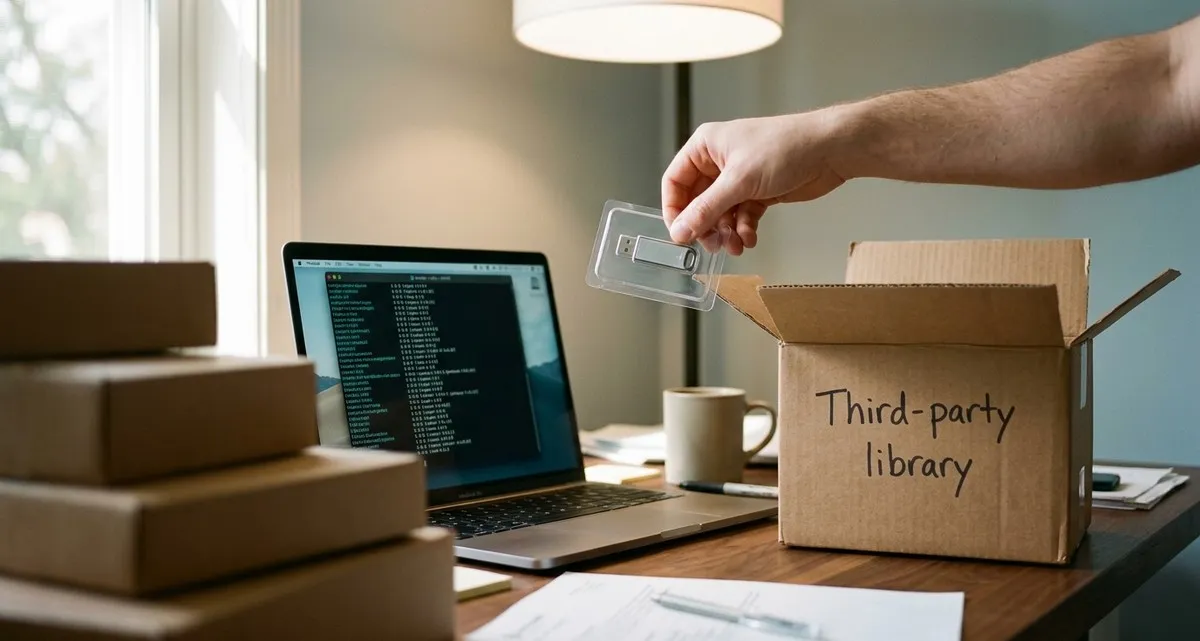
Supply‑chain attacks have become a top threat for any business that relies on third‑party software.
The headlines may sound distant, but the reality is simple: if a piece of software you rely on is compromised, the attackers can reach straight into your own systems – even if you never write a line of code yourself. For a bakery that uses an online ordering platform, a dentist’s practice that stores patient records in a cloud service, or a logistics firm that tracks deliveries with a third‑party routing tool, the risk is very real.
Practical audit checklist for third‑party components
You don’t need deep technical knowledge to start protecting yourself. Below is a concise checklist you can implement today, or hand over to your trusted IT provider.
-
Create an inventory of all external components
List every library, plugin, SaaS service, and development tool that touches your systems. Include version numbers and where they are hosted. -
Verify the source and signing
Prefer packages that are signed by a trusted maintainer and downloaded from official repositories. If a component is hosted on a public code‑sharing site, check that the maintainer’s identity is verified. -
Enable automated vulnerability scanning
Use a tool that regularly checks your inventory against known security advisories. Schedule scans at least weekly and act on any high‑severity findings within 48 hours. -
Implement strict access controls
Limit who can add or update third‑party components. Require multi‑factor authentication (an extra security step, like a code sent to a phone) for any account that can modify production environments. -
Conduct a periodic third‑party risk assessment
At least once a quarter, review the security posture of critical vendors. Ask for evidence of their own security monitoring, patch management, and incident‑response processes.
Immediate actions you can take now
- Update all software to the latest versions released by the vendor.
- Change passwords and enable multi‑factor authentication for any accounts that access third‑party tools.
- Run a full malware scan using a widely‑used tool such as a security scanner or SDK that you already trust.
Reducing third‑party risk for small businesses
A supply‑chain attack does not target you directly. Instead, the hackers infiltrate a trusted component that many companies use – a library, a scanner, a build tool – and hide malicious code inside it. When you download the latest version of that component, the hidden code runs on your servers, giving the attackers a foothold.
The widely‑used components targeted by the TeamPCP campaign showed how quickly the infection can spread:
- Self‑propagating malware – The worm, dubbed “Shai‑Hulud”, attached itself to future updates of compromised packages, so every new version carried the malicious payload.
- Credential harvesting – The malware stole authentication tokens from the infected machines, allowing the group to move laterally into other tools and services.
- Smart‑contract control – By using a flexible “canister” on the Internet Computer Protocol, the attackers could change the command‑and‑control URLs on the fly, making takedown attempts ineffective.
For a small business, the consequences can be severe: data theft, ransomware encryption, loss of customer trust, and costly downtime. Because the infection originates from a third‑party component, traditional security measures that focus only on your own servers often miss it.
FAQ: supply‑chain attack basics for small businesses
Q: I don’t develop software myself. Do I still need to worry about supply‑chain attacks?
A: Absolutely. Even if you only use off‑the‑shelf applications, those apps often rely on third‑party libraries. A compromise in one of those libraries can affect the whole application.
Q: How can I tell if a tool I use has been compromised?
A: Look for official security advisories from the tool’s maintainers, watch reputable security news sites, and run regular scans with a vulnerability‑checking service. Sudden changes in a tool’s download size or unexpected permission requests are also warning signs.
Q: My business can’t afford a full‑time security team. What’s the most cost‑effective way to stay safe?
A: Start with the checklist above and consider a managed security service that offers 24/7 monitoring and third‑party risk assessments. It provides expert oversight without the overhead of an in‑house team.
Protect your business with proactive monitoring
Supply‑chain attacks like those carried out by TeamPCP remind us that security is a shared responsibility. While you focus on serving customers and growing your business, IT Move NL’s 24/7 security monitoring and third‑party risk assessment service continuously watches the components you rely on, flags suspicious activity, and guides you through remediation. We’ll also provide a free security health check so you can see exactly where your vulnerabilities lie.
Get a free security health check
Don’t wait for the next headline to become your own crisis. Get in touch today, and let us help you secure the technology that powers your business.
Sources:

He/Him · AWS Certified Solutions Architect | Cloud Engineer @ Essent
Cloud Engineer at Essent B.V. with 10+ years of experience in the tech industry. AWS Certified, passionate about serverless architectures, Infrastructure as Code, and DevOps. Proficient in TypeScript, Python, and Terraform. Based in Amersfoort, Netherlands.
STAY IN THE LOOP
// Cloud, AI & DevOps insights — straight to your inbox.
No spam. Unsubscribe anytime.
// Related articles

Need help with your cloud infrastructure?
Our team of experts is ready to help you navigate the complexities of modern cloud architecture.
Get in Touch